Guides
EU data sovereignty for AI: what it actually takes
David Buxton · · 2 min read
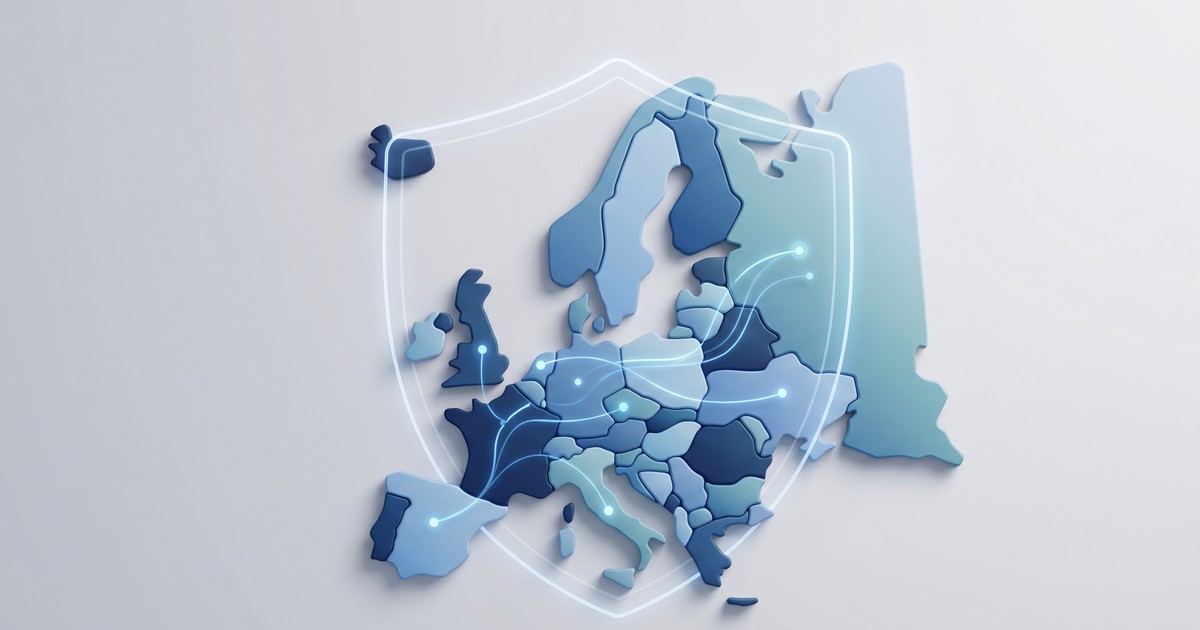
“Is our AI GDPR-compliant?” is becoming a board-level question across Europe. The honest answer at most companies is “we’re not sure”, because nobody knows where employee AI traffic actually goes.
The real problem isn’t the model, it’s the route
Most AI providers now offer EU-hosted inference. The harder problem is everything around the model: which employees are sending what, through which accounts, to which endpoints. A perfectly EU-resident model doesn’t help if half your staff are using personal accounts routed through who-knows-where.
Three things that need to be true
For a defensible data-sovereignty posture, you need:
- A single, known path. All AI traffic flows through infrastructure you control and can point to in an audit. No personal accounts, no rogue API keys.
- Region-pinned inference. Requests from EU entities route to EU-hosted models, enforced by policy, not by trust.
- Paper that matches reality. DPAs, sub-processor lists, and data-flow diagrams that describe the system you actually run, not the one you hope people use.
How Harriet approaches it
Harriet routes AI through approved regions at the platform level. The admin sets the policy once; every conversation on every endpoint follows it. Your DPO gets a data-flow story they can defend, and your employees get AI that just works. Harriet is SOC 2 Type II certified with EU data residency available, so the compliance paperwork lines up with the live system.
The reason this is enforceable at all is the control plane underneath: once every endpoint is provisioned through one path, region policy becomes something you set, not something you hope for.
Sovereignty doesn’t have to mean self-hosting everything. It means knowing, and being able to prove, where your data goes. Book a call to walk through your requirements with us.